
When Microsoft’s Latest Update Breaks the Desktop: What’s Happening and How to Fix It


If your users have recently logged into a Windows 11 session only to be greeted by a blank black screen, you’re far from alone. No taskbar, no Start menu, no desktop icons—just a lone mouse cursor floating over nothingness.
Microsoft recently confirmed a known issue tied to preview and cumulative updates across Windows 11 releases (specifically impacting versions 24H2, 25H2, and 26H1 via updates like KB5120996 and KB5120998).
The glitch mostly targets virtual desktop environments—especially Azure Virtual Desktop (AVD) hosts running FSLogix profile containers—leaving explorer.exe dead on arrival during logon.
Here is what’s going on under the hood, how users can jump-start their desktops in a pinch, and the exact steps to roll back the bad code across your estate using Microsoft's Known Issue Rollback (KIR).
What’s Actually Breaking?
When a user logs in, Windows relies on explorer.exe to spin up the interactive user interface. Following these recent updates, the process crashes right at startup.
If you check the Event Viewer on an affected machine under Windows Logs > Application, you’ll likely find crash events pointing straight at Explorer. The user's underlying session is technically active in the background, but without a running shell, the screen stays completely black.
The Quick User Fix (When Someone Is Stuck Right Now)
If you have a user stuck staring at a black screen on a call, you don't need to reboot the server or blow away their FSLogix profile. You can launch the shell manually:
Press Ctrl + Shift + Esc to open Task Manager.
Click Run new task (or File > Run new task).
Type explorer.exe and hit Enter.
Within a couple of seconds, the taskbar and desktop icons should pop right back up.
Fix It at Scale: Deploying the Known Issue Rollback (KIR)
While Microsoft works on a permanent patch in an upcoming update, they’ve issued a Known Issue Rollback (KIR) to disable the problematic feature flag.
If you manage devices or session hosts via Active Directory, here is how to deploy the rollback policy step-by-step.
Step 1: Grab the Policy Template
Microsoft delivers KIR fixes as .msi installers containing Group Policy ADMX/ADML files.
Download the specific KIR Group Policy package linked in the Microsoft Release Health dashboard or KB article for your OS build (e.g., KB5120996 / KB5120998).
Run the .msi on your management host or Domain Controller.
By default, it extracts files to:
C:\Program Files (x86)\Microsoft Group Policy\
Step 2: Copy Files to Your Central Store
To ensure all your Domain Controllers can see the new settings, drop the extracted files into your SYSVOL Central Store:
Copy the .admx file to:
\\YourDomain.com\SYSVOL\YourDomain.com\policies\PolicyDefinitions\
Copy the .adml file to the appropriate language folder (e.g., en-US):
\\YourDomain.com\SYSVOL\YourDomain.com\policies\PolicyDefinitions\en-US\
(If you don't use a Central Store, place them directly in C:\Windows\PolicyDefinitions on the machine where you run Group Policy Management).
Step 3: Configure the GPO
Open Group Policy Management (gpmc.msc).
Right-click the Organizational Unit (OU) holding your affected session hosts or endpoints, and select Create a GPO in this domain, and Link it here...
Name it something clear, like KIR - Windows 11 Desktop Fix (KB5120996).
Right-click the new GPO and select Edit.
Navigate to:
Computer Configuration > Policies > Administrative Templates > [Folder Name named after the KB/Issue]
Open the policy setting, set it to Disabled (or follow the exact toggle state specified in Microsoft's KB notes for that release), and save.
Step 4: Update Policy and Reboot Host
KIR policies modify internal OS feature flags, meaning they generally won't take effect until the machine actually restarts.
Open an elevated command prompt on the host and run:

DOS
gpupdate /force
Reboot the host:
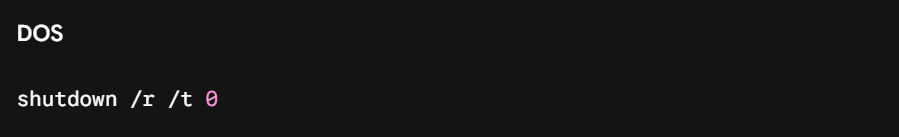
DOS
shutdown /r /t
Once restarted, test a logon with an affected profile to verify that explorer.exe initializes cleanly without manual intervention.
Next Steps
Keep this GPO linked until Microsoft rolls out the official permanent fix in a future cumulative update. Once you've patched your fleet with the permanent fix down the road, you can safely remove the KIR GPO to keep your policy structure clean.


Comments